Reduce alert fatigue, accelerate investigations, and orchestrate consistent response with intelligent SOC Automation designed for modern cloud, network, and endpoint environments.
Built to integrate with Security Information and Event Management (SIEM), EDR, cloud security, and ticketing workflows.
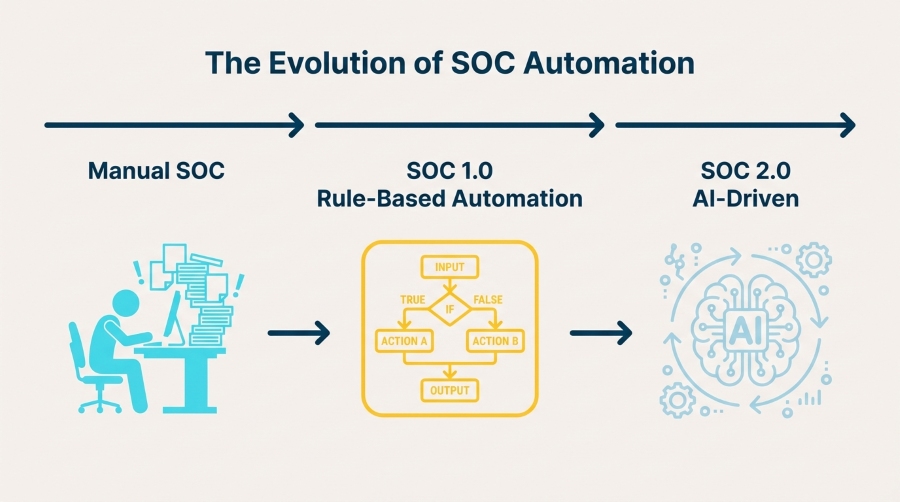
repetitive triage tasks automated
response-ready playbook execution
faster investigation handoffs
missed escalation steps
Unify detection, enrichment, prioritization, and response into repeatable workflows that help analysts focus on decisions instead of manual tasks.
Automatically enrich alerts with asset context, identity data, threat intelligence, and business impact signals.
Standardize investigations with approved response steps, escalation rules, and audit-ready documentation.
Trigger safe containment actions for suspicious users, hosts, domains, or workloads after analyst approval.
Connect automation across SIEM, SOAR, EDR, firewalls, IAM, cloud platforms, and service desk systems.
Track mean time to detect, mean time to respond, false positive trends, and automation coverage.
Preserve response records and control evidence to support frameworks such as SOC 2.
.
Proactively surface hidden adversaries by continuously matching environment telemetry against the latest global indicators of compromise (IoCs) and behavioral anomalies.
Feed resolution outcomes back into detection engines to fine-tune alert thresholds, permanently reducing false positives and noise.
We design SOC Automation around your people, tools, risk priorities, and response maturity—then tune it continuously so workflows stay useful as threats evolve.
Identify high-volume alerts, manual handoffs, escalation bottlenecks, and risk-based response priorities.
Create playbooks with approvals, rollback paths, and clear decision points before fully automated actions.
Connect signals from detection tools and route actions into Incident Case Management for traceable response.
Tune playbooks, reduce false positives, and expand automation coverage with operational metrics.
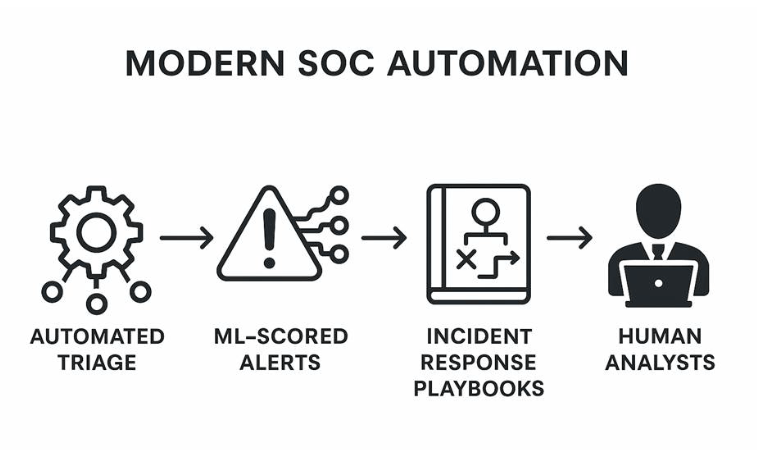
SOC Automation is most effective when it supports broader detection, prevention, and response strategy. Physics Cyber helps teams mature from isolated alerts to measurable security operations.
We can align SOC workflows with Intrusion Detection and Prevention, Network Security Automation, and targeted response for high-risk threats like ransomware.
“The goal is not to automate every decision. The goal is to automate the repeatable work so analysts can make better decisions faster.”
Physics Cyber SOC Automation Team
Practical answers for security leaders planning automation without sacrificing control.
No. It removes repetitive enrichment, routing, and documentation tasks so analysts can spend more time on validation, threat hunting, and strategic response.
Yes. We design integrations around your existing SIEM, EDR, cloud platforms, identity tools, network controls, and service desk workflows.
We start with human-in-the-loop approvals, severity thresholds, clear rollback steps, and phased automation before enabling direct containment.
Track time to triage, response time, escalation accuracy, false positive rate, analyst workload, control evidence quality, and playbook adoption.
Tell us about your current SOC tools, alert volume, and response goals. We will help identify high-value automation opportunities and practical next steps.
We reply within 24h.
Start with high-impact SOC Automation that reduces noise, improves response confidence, and scales with your security operations maturity.
With a focus on cyber security and reliable server solutions, we deliver trusted services that keep your systems running smoothly and your data protected.