Physics Cyber helps organizations prevent, detect, contain, and recover from ransomware with layered security controls, expert monitoring, tested playbooks, and resilient backup strategy.
Built for executives, IT teams, and security leaders who need measurable risk reduction before an incident becomes business disruption.
Our ransomware protection program creates an even, practical defense model across prevention, visibility, response, and recovery.
Monitoring for suspicious behavior, privilege abuse, and lateral movement
Core layers: endpoints, identities, networks, and backups
Targeted triage cadence for high-risk alerts and containment decisions
Trust assumptions reduced through least privilege and verification
Ransomware is not stopped by one tool. We align security architecture, monitoring, hardening, and recovery so every control supports the next.
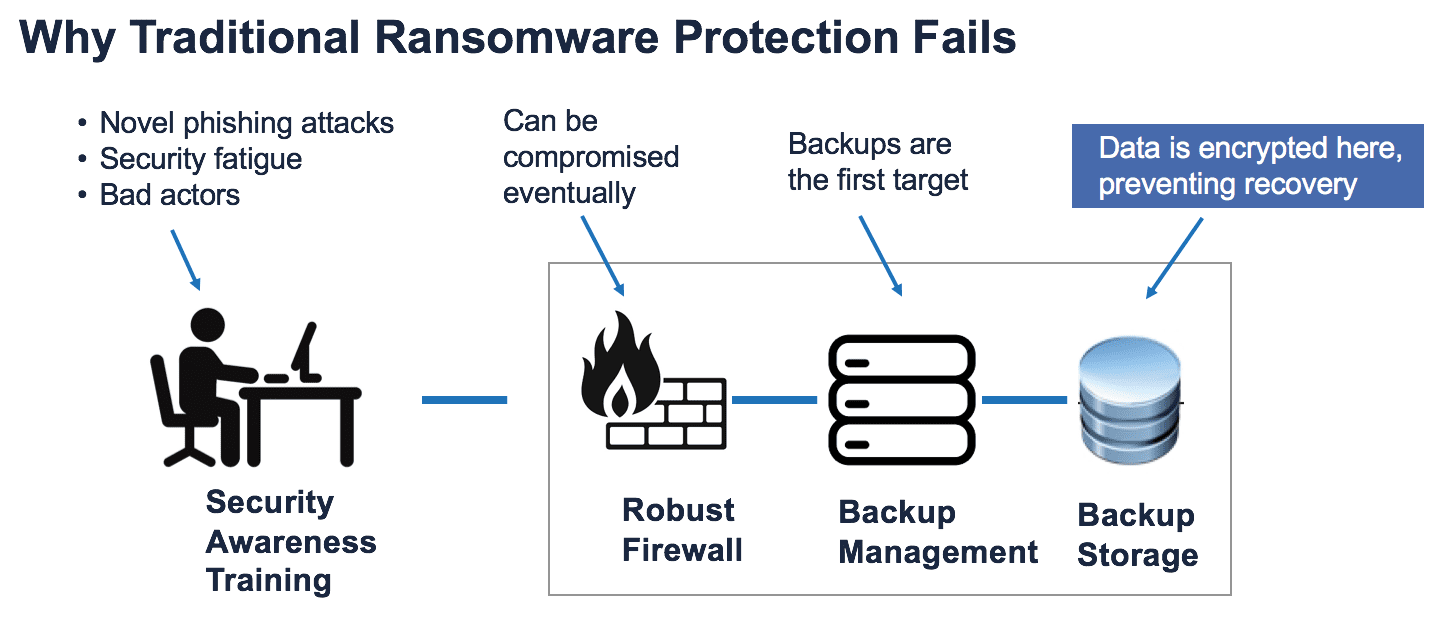
Strengthen devices with policy baselines, exploit reduction, EDR tuning, and Endpoint Protection.
Reduce credential misuse with MFA, privileged access review, conditional access, and least-privilege enforcement.
Turn logs into action with tuned alerts, correlation, and Security Information and Event Management (SIEM).
Escalate with confidence using containment playbooks, evidence handling, and Managed Detection & Response.
Validate immutable backups, restore priorities, recovery objectives, and offline access procedures before crisis day.
Map controls to executive risk, cyber insurance expectations, tabletop exercises, and SOC 2 readiness.
Minimize exposure by mapping external assets, closing unused ports, patching vulnerabilities, and disabling legacy protocols.
Build security culture with targeted phishing simulations, role-based awareness training, and clear internal reporting channels.
We start with business impact, then engineer the controls that protect the systems, data, and people most likely to be targeted.
Review attack surface, endpoints, privileged access, backups, SaaS, cloud, and known ransomware pathways.
Close the highest-risk gaps first with secure configuration, segmentation, identity controls, and detection rules.
Use alerts, escalation paths, and response actions to stop encryption and lateral movement fast.
Run post-incident lessons, restore validation, control tuning, and executive reporting.
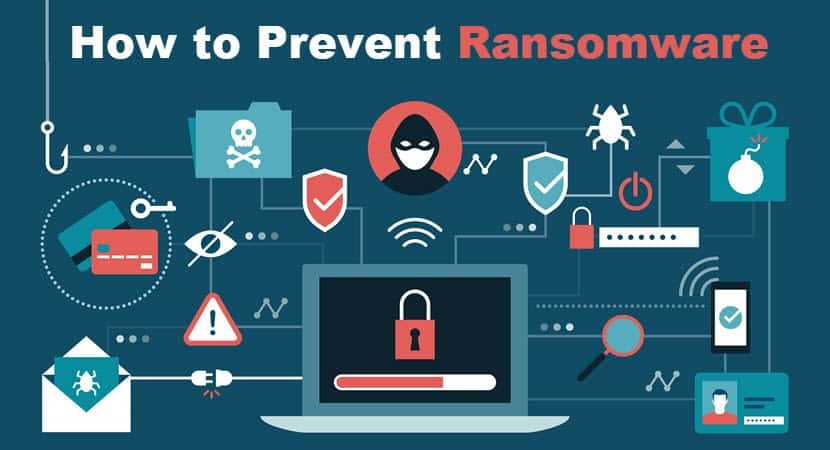
Modern attackers target backups, administrators, cloud consoles, and business-critical workflows. Our program connects technical defense to continuity planning so recovery decisions are faster and safer.
If you are improving existing controls, we can also help ransomware risk analysis connect to board reporting and operational priorities.
Use these questions to plan your next security discussion with IT, leadership, and incident response stakeholders.
Yes. Antivirus is only one layer. Ransomware protection also requires identity controls, monitoring, network containment, tested backups, and response procedures.
Most organizations can begin with a focused discovery session, asset review, and prioritized roadmap before moving into implementation and monitoring.
We help teams triage suspicious activity, preserve evidence, coordinate containment, and improve workflows with Incident Case Management.
Start with identity providers, administrator workstations, endpoint fleets, backup platforms, cloud consoles, core applications, and critical file repositories.
Tell us what you want to protect. We reply within 24h.
Build a practical ransomware protection roadmap that strengthens prevention, accelerates response, and protects recovery options.
With a focus on cyber security and reliable server solutions, we deliver trusted services that keep your systems running smoothly and your data protected.