Reduce manual effort, improve response speed, and standardize controls with Network Security Automation designed for hybrid networks, cloud environments, branch locations, and security operations teams that need repeatable outcomes.
Built for teams modernizing detection, policy enforcement, and response without adding operational complexity.
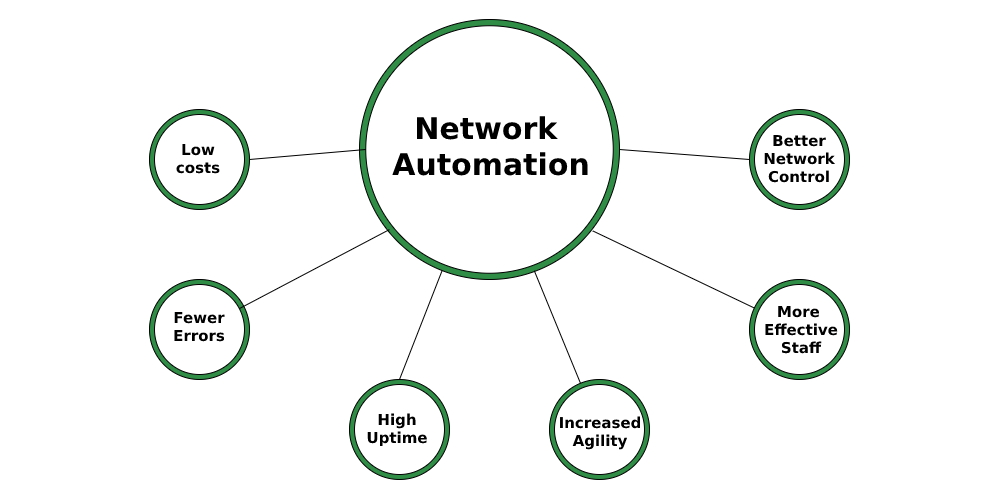
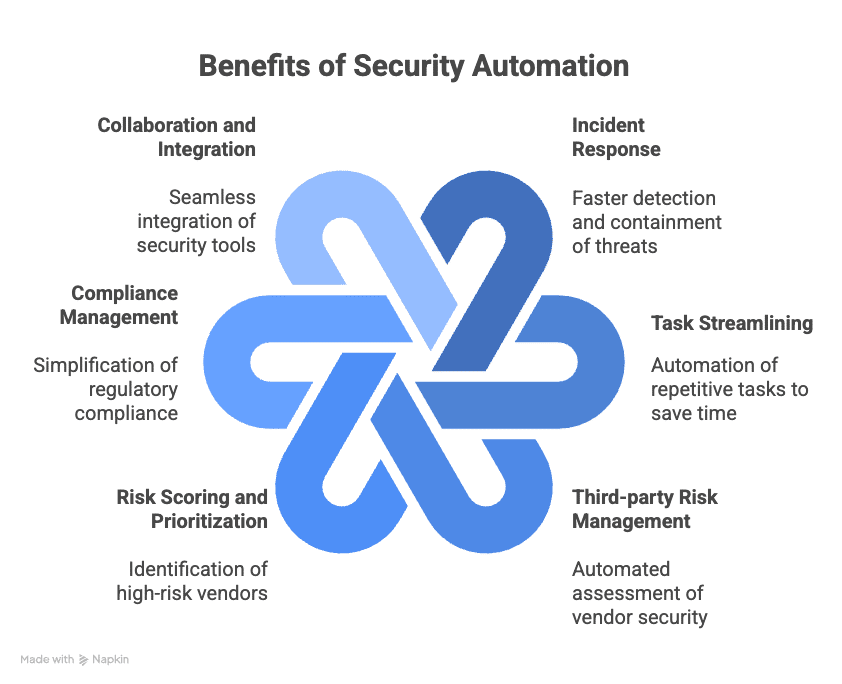
fewer repetitive security tasks through workflow orchestration
policy checks, alert enrichment, and automated response support
faster triage with consistent playbooks and integrated tooling
auditable automation logic aligned to your risk and compliance needs
Physics Cyber designs automation that connects people, policies, signals, and response systems so your team can act with confidence instead of chasing fragmented alerts.
Translate approved security rules into repeatable workflows for firewalls, cloud controls, endpoints, and network segments.
Enrich alerts, prioritize threats, open tickets, isolate suspicious assets, and escalate severe events with integrations for Security Information and Event Management (SIEM).
Automate asset discovery, service validation, and attack-surface checks using proven approaches that complement tools like Shodan.
Connect automation to Intrusion Detection and Prevention, DNS filtering, and segmentation so threats are contained earlier.
We build practical automation in controlled phases, so every playbook is measurable, approved, and safe to operate in production.
Identify devices, applications, cloud services, identities, security tools, and the manual workflows slowing your team down.
Define decision logic, approval gates, rollback plans, and escalation paths before automation touches production controls.
Connect APIs, logs, ticketing, notification systems, and security controls, then validate each workflow under realistic scenarios.
Measure false positives, response time, control accuracy, and audit quality so your automation improves over time.
Security automation is not just about speed. It gives your team a reliable operating model: clear ownership, predictable workflows, consistent evidence, and fewer high-risk manual actions during urgent incidents.
“The best automation removes uncertainty. It helps analysts make better decisions faster, while keeping business-critical services protected.”
Physics Cyber Security Engineering Team
Straight answers for leaders planning to automate security operations without losing control.
Common starting points include alert enrichment, ticket creation, asset lookups, firewall request validation, phishing response, and vulnerability triage.
No. Automation removes repetitive work and gives analysts better context, while humans remain responsible for strategy, approvals, and high-impact decisions.
We use approval gates, testing, logging, least-privilege access, rollback plans, and staged deployment so automated actions remain controlled.
Yes. Automation can support DNS investigations, policy enforcement, cloud alerts, and control validation, including programs related to DNS Security.
Tell us about your network, tools, and current workflows. We will help you identify high-value automation opportunities and a practical implementation path.
We reply within 24h.
With a focus on cyber security and reliable server solutions, we deliver trusted services that keep your systems running smoothly and your data protected.